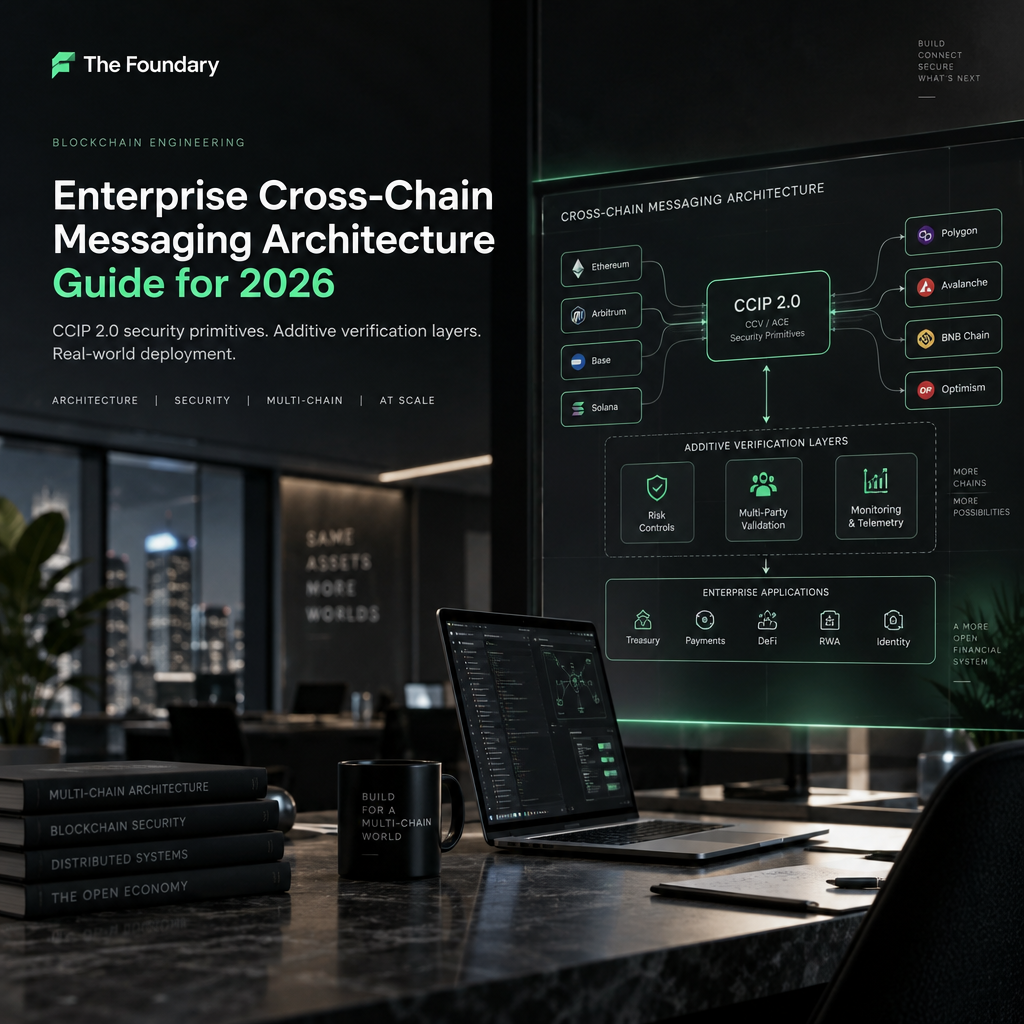
Architecting an enterprise cross-chain messaging architecture now requires deeper attention to verification and compliance protocols. The launch of CCIP 2.0 on September 28, 2026 marked a turning point for institutional transfers and risk management. This update introduced configurable security verifiers and new compliance controls that address recent vulnerabilities in the sector. You must evaluate these primitives to ensure your systems can handle the growing volume of cross-chain value safely. As we look at current data, Chainlink has secured more than $84 billion in total cross-chain token value as of launch. This figure underscores the scale of trust placed in these messaging layers daily. The ecosystem has expanded to 80+ networks supported as of September 29, 2026. We will explore how to implement these standards without introducing unnecessary complexity to your stack.
Understanding the Shift to CCIP 2.0
The most significant change arrived with CCIP 2.0 at Sibos 2026 in Miami. The upgrade introduced Cross-Chain Verifiers allowing institutions to operate their own verification layer on top of Chainlink’s default 16-operator Committee Verifier. This shift came five months after the $292 million KelpDAO exploit attributed to North Korean-affiliated hackers reshaped industry priorities. Chainlink replaced its Risk Management Network with optional CCVs that issuers can configure or outsource. Pre-built starter kits for CCVs are available for Amazon Web Services and Google Cloud to speed up adoption. Existing CCIP integrations continue to work with CCIP 2.0 without changes ensuring migration remains smooth. This backward compatibility is vital for teams that cannot afford downtime during upgrades. The infrastructure is certified to ISO 27001 and SOC 2 Type 2 meeting rigorous enterprise security standards. You can rely on these certifications when presenting risk assessments to your board.
Additive Security Models and Verification Layers
Traditional bridges often relied on single points of failure within their validator sets. Additive security models allow you to chain verification requirements before execution. Cross-chain verifiers act as additional guards that validate messages against your specific policies. Third-party CCV operators can set custom verification fees on top of CCIP’s base fee rate. This flexibility means you can pay for higher security tiers if your asset volume demands it. Infosys and Nethermind are building CCV offerings for institutional clients to meet diverse needs. These providers bring deep expertise in compliance and infrastructure management. You can deploy a starter kit locally and then connect it to the wider network. The process isolates risk by letting you approve transactions before they settle on the destination chain. This design reduces the surface area available for attackers to exploit during transit.
Configuring the Automated Compliance Engine
The Automated Compliance Engine enables KYC, AML, sanctions screening, and transaction limits at the protocol level. You define rules that filter outbound transfers based on user identity and source funds. This capability helps teams avoid regulatory breaches while maintaining smooth transfers. Configuration requires internal risk policies mapped to ACE rules and KYC/AML screening setup. Chainlink CCIP aligns with ISO 20022 global financial messaging standards ensuring global interoperability. The engine supports transaction limits that block high-risk transfers automatically without human intervention. Pre-built configurations exist for major regulatory frameworks to simplify initial setup. You must test these rules on testnet before enabling them for production assets. This step prevents legitimate transfers from being rejected due to overly strict initial parameters.
Implementing Additive Security for High Value
For assets exceeding standard thresholds, you should enforce stricter verification requirements. Define verification policies such as threshold approvals for transfers above $1 million. This approach ensures high-value movements receive multiple independent checks before execution. You can require signatures from multiple authorized users or systems before a transfer passes. The system supports faster-than-finality transfers with configurable settlement windows for low-risk movements. This feature allows teams to optimize speed while maintaining a safety net for large sums. Chainlink CCIP 2.0 supports faster-than-finality transfers with configurable settlement windows to balance speed and safety. You can tune these windows based on the destination chain performance and your internal risk appetite. Monitoring for CCV attestation failures becomes a core operational task in this setup. Teams should set alerts for any verification step that takes longer than the agreed SLA.
Protocol Comparisons for Enterprise Selection
Choosing the right protocol depends on your specific needs for speed compliance and network reach. The table below compares CCIP 2.0 against other major players in the interoperability space.
| Platform | Trust Model | Primary Use Case | Network Coverage | Settlement Speed | Compliance Tools |
|---|---|---|---|---|---|
| Chainlink CCIP 2.0 | 16-operator Committee Verifier + optional CCVs | Institutional tokenized assets | 80+ networks | Configurable (seconds to full finality) | Built-in ACE (KYC, AML, sanctions) |
| LayerZero v2 | Decentralized Verifier Network (DVN) | Omnichain tokens (OFT) | 70+ chains | ~30s-2min | Configurable via OApp |
| Hyperlane | Interchain Security Modules (ISMs) | Modular message-only | 140+ chains (mid-2026) | ~1-3 min | Customizable per ISM |
| Wormhole | Guardian network (19 fixed validators) | Message + liquidity | 30+ chains | ~1-5 min | Limited native compliance |
| Axelar | PoS validators (hub-and-spoke) | General Message Passing | Broad Cosmos + EVM | 1-2 min | Custom smart contracts |
CCIP 2.0 leads in compliance tools with built-in ACE features. This makes it a strong candidate for teams needing to meet financial regulations immediately. Network coverage is broad enough to support most enterprise use cases. Settlement speed is configurable which is a distinct advantage over fixed models. The trust model offers a balance between decentralization and institutional control. You should review these factors against your internal security policies before signing contracts.
Step-by-Step Deployment Timeline
Deploying this stack follows a structured timeline to ensure security and compliance are verified. You should allocate seven weeks for a full rollout from assessment to production.
- Week 1: Assess existing CCIP integration and define security requirements for CCVs.
- Week 2-3: Deploy CCV starter kit on AWS or Google Cloud and configure ACE compliance rules.
- Week 4: Define verification policies such as threshold approvals for transfers above $1M.
- Week 5: Test on testnet with custom CCV signatures to validate signing logic.
- Week 6: Production rollout with staged migration and monitor for CCV attestation failures.
- Week 7+: Enable faster-than-finality transfers for low-risk transactions and establish CCV marketplace selection.
This process minimizes disruption to active channels. You will need access to cloud infrastructure and smart contract development skills. Internal teams should map compliance prerequisites early to avoid delays. Partner ecosystems including Fidelity International and ANZ Bank are already supporting these standards. You can reach out to them for insights on implementation patterns. This timeline assumes you have defined risk policies ready for ACE configuration.
Cost Models and Infrastructure Needs
Understanding costs is essential when scaling cross-chain operations across multiple chains. CCIP base fees include gas plus node operator percentage fee plus fixed overhead. This overhead varies by chain and the complexity of the transfer request. Third-party CCV operators can charge custom verification fees on top of base rate. You will need AWS or Google Cloud VMs for CCV operation to run your local layer. Starter kits simplify the setup but you still need to manage the underlying infrastructure costs. Migration cost is low because existing CCIP integrations require no changes to work. ROI factors include reduced bridge vulnerability exposure and compliance automation features. Support for 80+ networks with single integration reduces development time significantly. You should model these costs against the security gains your team expects to realize. There is no explicit published pricing table available for CCIP 2.0 enterprise licensing yet. Teams should contact vendors directly for specific enterprise agreements and volume discounts.
Meeting Enterprise Blockchain Interoperability Standards
Institutions need to align with global financial standards to operate effectively. Chainlink CCIP aligns with ISO 20022 global financial messaging standards for structured data. This alignment ensures your transfers can integrate with traditional banking rails if needed. It simplifies auditing and reporting for external regulators and internal teams. You will find that this standard supports rich metadata and clear transaction references. The 24 financial institutions and market infrastructure providers as partners show industry adoption. Partner ecosystems include entities like DTCC and SWIFT that operate within these frameworks. Using a standard compliant system reduces friction when onboarding new partners. It also ensures your architecture remains future proof as regulations evolve globally.
Finalizing Your Security Stack
Securing your enterprise cross-chain messaging architecture requires a layered approach to verification. You have the tools to deploy custom verifiers and enforce compliance rules automatically. The combination of CCVs and ACE offers a strong foundation for institutional transfers. Teams should monitor network coverage and settlement speed as part of their operational health checks. Staying aligned with the latest security research and updates from vendors like Chainlink ensures resilience. You must verify that your cloud infrastructure meets the necessary certifications for your jurisdiction. The journey to full compliance and security takes time but the benefits are substantial. For more support on your engineering path, you can visit The Foundary, Engineering Digital Foundations to learn how we approach digital infrastructure.
Talk to a Foundry engineer
If you are planning a multi-chain deployment, reach out to The Foundary to discuss your platform or AI project. Talk to The Foundary about blockchain
Conclusion
Secure cross-chain messaging requires more than basic connectivity. You must implement verification layers and compliance tools to manage risk effectively. The new primitives allow you to tailor security to your specific asset classes. Start by mapping your internal policies to the available automated controls.
Frequently Asked Questions!
1. How do CCVs prevent single-point-of-failure vulnerabilities compared to traditional bridges?
Cross-chain verifiers allow you to operate your own verification layer on top of default operators. This creates additive security models where multiple independent nodes must approve a transaction.
2. What happens when a required CCV is unavailable or unresponsive during a transfer?
Transfers may pause until the verification step is satisfied. You should configure timeout rules and monitor for attestation failures in your operations dashboard.
3. How can institutions configure ACE to meet specific regulatory requirements?
The Automated Compliance Engine enables KYC, AML, sanctions screening and transaction limits. You define internal risk policies mapped to ACE rules and KYC/AML screening configuration.
4. What is the gas cost difference between CCIP transfers with and without CCVs?
Third-party CCV operators can set custom verification fees on top of CCIP base fee rate. Exact gas cost differences between CCIP transfers with or without CCVs are not quantified publicly.
5. Can CCVs be chained together requiring multiple verifiers before execution?
Yes. You can enforce threshold approvals for transfers above specific amounts. This allows you to chain multiple verification requirements for high value movements.
6. How does CCIP 2.0 handle cross-chain transfers between private and public blockchains?
The protocol supports over 80 networks and allows configurable compliance. Private chains can integrate via standard interfaces with verification rules set on your CCV layer.
By the Foundry Engineering Team · Updated 2026-10-06