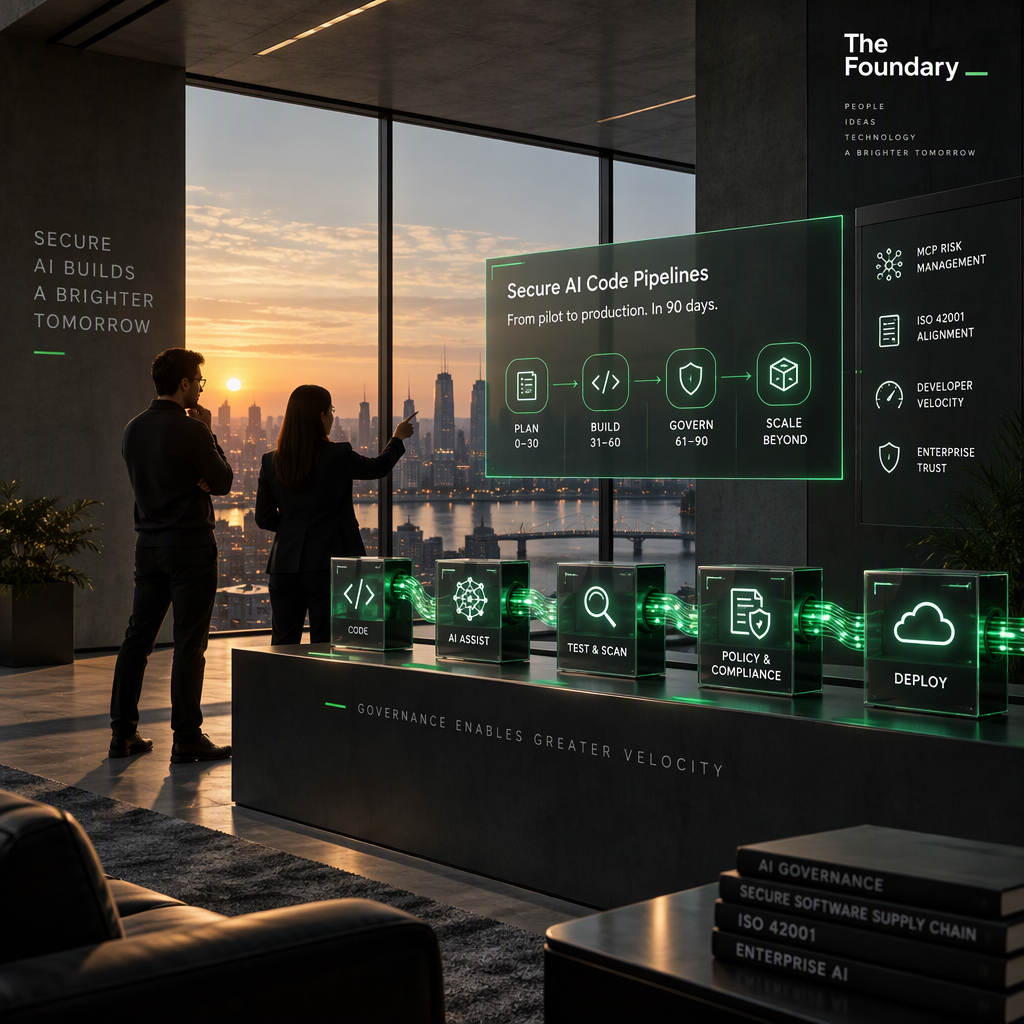
Organizations must learn how to secure ai code pipelines to prevent vulnerabilities in modern development workflows. Recent data shows stagnation in security pass rates despite improved code quality. You face risks from Model Context Protocol servers and unvetted dependencies. This guide offers a structured approach to manage those risks without slowing delivery. We will examine standards and tools to harden your infrastructure.",
The Current State of AI Code Security
Recent benchmarks indicate that security pass rates remain flat despite increased adoption. Veracode released the 2026 GenAI Code Security Report showing that AI-generated code security pass rates have remained stagnant at 56% since 2023 despite syntactic improvements. This stat holds across more than 100 models tested as of July 28, 2026. Roughly 44% of AI code generation tasks introduced a risky security vulnerability in tests when no specific security guidance was given during those assessments. Tools now generate roughly half of all newly committed code across organizations scanned in the report. Java has the lowest security pass rate among major languages at only 30% despite showing the clearest upward trend over the past year. You cannot assume higher quality just because generation speeds have increased.
Why Model Context Protocol Servers Introduce Risk
MCP servers allow models to interact with external tools and data sources. This capability expands the attack surface significantly if not managed correctly. The MCP Spec states that Model Context Protocol (MCP) servers implementing authorization must verify all inbound requests and must NOT treat possession of a state handle as authentication as of July 28, 2026. OAuth 2.1 with audience-bound tokens is required for secure remote MCP server communication to prevent token passthrough vulnerabilities according to security guidelines. Attackers could exploit weak authentication to access sensitive data or execute unauthorized commands. You must enforce strict authorization checks and audit logs for every request your agents make. Treating any handle as proof of identity leaves your system exposed to takeover.
Building an Enterprise AI Code Security Framework
A successful strategy combines technology with clear governance policies. You need a framework that addresses risk management and lifecycle oversight consistently. ISO/IEC 42001 defines 38 controls grouped into nine areas in Annex A, covering AI policy, lifecycle management, and data governance as of 2026. These controls provide a structured path to certification and regulatory alignment. Your team must identify which controls apply to your specific risk profile and workflow. Mapping these controls to existing security policies reduces duplication and effort. A framework ensures everyone understands their role in maintaining safety across projects.
Enabling CI/CD Gates for AI Tools
You must integrate specific checks into your existing build processes to catch issues early. AI-aware Static Application Security Testing (SAST) and Software Composition Analysis (SCA) are mandatory gates that must be integrated as a blocking step in the CI pipeline before dependencies are installed as of July 16, 2026. Blocking steps prevent risky code from advancing to production environments. Logging must be wired to SIEM tools to track patterns and anomalies over time. GitHub Actions and GitLab CI are standard pipelines that support these integrations easily. Failing to block at the pipeline stage increases the chance of exposure in deployment.
Aligning With ISO 42001 Controls
ISO 42001 certification provides a framework for governance that many enterprises now require. Alignment with EU AI Act requirements (Annex III) is critical for high-risk systems in many jurisdictions. Your organization should formalize AI governance policy aligned with ISO/IEC 42001 controls to meet these mandates. You need proficiency in AI risk management, prompt injection testing, and ISO 42001 control implementation across your teams. Training sessions help engineers understand how these controls apply to daily tasks. Without proper alignment you risk non-compliance fines and reputational damage.
Platform Comparison for Security Gates
Different tools offer varying capabilities for code analysis and compliance. Selecting the right platform depends on your specific needs and existing stack.
| Platform | Key Capability | Best For | DevEx Integration | Custom Rule Support |
|---|---|---|---|---|
| SonarQube | Dedicated AI Code Quality Gate | Quality Gates & Security Ratings | IDE & CI/CD | Yes |
| Semgrep | Custom Security Rules | Targeting AI Anti-Patterns | IDE & CI/CD | High |
| Snyk | Code, Dependencies, & Container Scanning | Supply Chain Security | IDE & CI/CD | Moderate |
| Checkmarx | SAST & DAST | Enterprise Governance | CI/CD | High |
| GitHub Advanced Security | Native Secret Scanning | GitHub Repositories | Native Integration | High |
You should evaluate these options against your team size and regulatory requirements. Larger teams often benefit from custom rule support and deep integration.
A 90-Day Phased Rollout Plan
Follow this timeline to implement changes without disrupting active projects.
- Phase 1: Days 1-30 identify all AI coding tools and agents currently in use and enable AI-authored code tagging in repositories. Configure mandatory secret scanning on all pre-commit hooks and pull requests immediately.
- Phase 2: Days 31-60 integrate AI-aware SAST and SCA tools into the CI pipeline as blocking gates. Enforce OAuth 2.1 authentication for all remote MCP servers to ensure secure communication.
- Phase 3: Days 61-90 formalize AI governance policy aligned with ISO/IEC 42001 controls. Implement sandboxed execution environments for all AI agents to isolate risks. ## Cost and Resource Planning for Implementation Building a custom SAST pipeline is viable for large internal teams but buying offers faster time to market. Enterprise tool licensing typically scales with developer seat count and repository size. Secure execution environments like containers or MicroVMs add compute costs but reduce breach remediation costs. Security engineers require training on AI-specific vulnerabilities to maintain gates effectively. You should plan for ongoing expenses related to software licenses and staffing needs. ## Planning For Long-Term AI Security You must anticipate future changes in model capabilities and threat vectors. Organizations are moving from pilot to production by implementing mandatory SSO, audit logging, and secret scanning for AI agents. 88% of enterprise AI agent pilots never reach production due to governance gaps and infrastructure risks rather than model quality issues. Your focus should be on reducing those governance gaps through clear policies. Regular audits help keep your defenses aligned with evolving standards and requirements. ## Key Takeaways for Engineering Leaders You can secure your AI integration by following structured rollout and governance steps. Stagnant pass rates highlight the need for mandatory CI/CD gates and verification. Tools like SAST and SCA must block deployment until checks clear. Model Context Protocol security requires strict OAuth 2.1 controls and request verification. ISO 42001 alignment provides a solid foundation for compliance and policy. Plan your resources carefully to support these changes over time. ## Resources For Further Implementation You can review the full Veracode report for more details on pass rates at https://www.veracode.com/blog/2026-genai-code-security-report-ai-risk/. For MCP security specifics refer to the official guidance at https://modelcontextprotocol.io/docs/2026-07-28/tutorials/security/security_best_practices. Additional pipeline guidance is available from https://bestdefense.io/blog/securing-ai-written-code-in-your-pipeline/.
Talk to a Foundry engineer
If you are ready to upgrade your engineering stack we can help you design a secure architecture. Talk to The Foundary about your build
Conclusion
Securing AI code pipelines requires more than just scanning output. It demands a structured approach combining CI/CD gates and ISO 42001 alignment. You must prioritize MCP security and mandatory blocking checks. By following this 90-day plan you reduce risks while maintaining velocity. Consistency in enforcement is the only way to improve pass rates.
Frequently Asked Questions!
1. How do we distinguish between AI-generated and human-written code in a merged commit?
You can enable AI-authored code tagging in your repositories during the audit phase. This feature flags commits that originated from AI tools so scanners can prioritize them for review.
2. Do we need separate security scans for AI-authored code compared to human-authored code?
Best practices recommend integrating AI-aware SAST and SCA tools as mandatory gates for all pipelines. This ensures consistent coverage regardless of the source of the code changes.
3. Can we use MCP servers for sensitive operations without a Human-in-the-Loop approval?
No. Security standards advise enforcing strict authorization checks and OAuth 2.1 tokens to prevent unauthorized access. Sensitive operations should require explicit user approval or sandboxed execution.
4. How do we handle token passthrough risks if an MCP server accepts credentials from a client?
You must treat state handles as unverified and validate all inbound requests separately. Using OAuth 2.1 with audience-bound tokens prevents clients from passing credentials that bypass your checks.
5. What is the recommended strategy for preventing prompt injection in tool outputs?
Isolate agent execution in sandboxed environments and validate output before processing. Training on prompt injection testing is part of the required skill set for your security team.
6. How do we map ISO 42001 controls to existing ISO 27001 security policies?
Start by identifying overlaps in risk management and policy areas. You can extend existing controls to cover AI lifecycle management and data governance as defined in Annex A.
By the Foundry Engineering Team · Updated 2026-10-04